Management Guidelines for Major Topics
Information Security Management
| Item | Explanation |
|---|---|
| Information Security Management | |
| Information Security Management |
Advantech is a global leader in the IoT industry. Information security directly affects our operational stability and product security, both of which are extremely important to our brand value, employees, customers, and investors. In addition, the FSC amended the law to clearly stipulate information security requirements for listed companies, which are required to make a material information announcement when a major information security incident occurs. |
| Policy or commitment | |
| Policy or commitment |
Advantech deeply recognizes that information security is the cornerstone of corporate sustainability and the trust of stakeholders. Facing the information security risks brought by digitization and the rapid development of cloud applications, one of our core business strategies is to continue strengthening information security governance and protection capabilities.
|
| Positive impact | |
| Positive impact |
Recognizing the positive impacts and growing importance of information security within the technology supply chain, Advantech’s efforts to strengthen cybersecurity build customer confidence while reinforcing overall risk management and operational resilience. |
| Negative impact | |
| Negative impact |
Information security breaches can negatively impact business operations through the leakage of confidential information and system service interruptions, which can damage Advantech’s reputation, result in a loss of business and customers, and create litigation risks.
|
| Actions in response to negative impacts that occur | |
| Actions in response to negative impacts that occur |
When an information security incident (such as data leakage) occurs, the organization immediately activates a response mechanism, isolates the affected system to prevent its spread, and investigates the incident while assessing losses. The incident is reported internally to management, while the competent authorities and affected users are notified externally in accordance with regulations, with remedial measures promptly provided. Following an incident, vulnerabilities are reviewed, and controls and training are strengthened to reduce the risk of recurrence. |
| Overview of target achievement in 2025 | |
| Overview of target achievement in 2025 |
|
| 2026 targets | |
| 2026 targets |
|
| 2030 Goals | |
| 2030 Goals |
|
| Key action plans or programs in 2025 | |
| Key action plans or programs in 2025 |
|
| Effectiveness evaluation | |
| Effectiveness evaluation |
|
| Stakeholders affected by this material topic and actions taken by Advantech | |
| Stakeholders affected by this material topic and actions taken by Advantech |
|
Information Security Policy and Organization
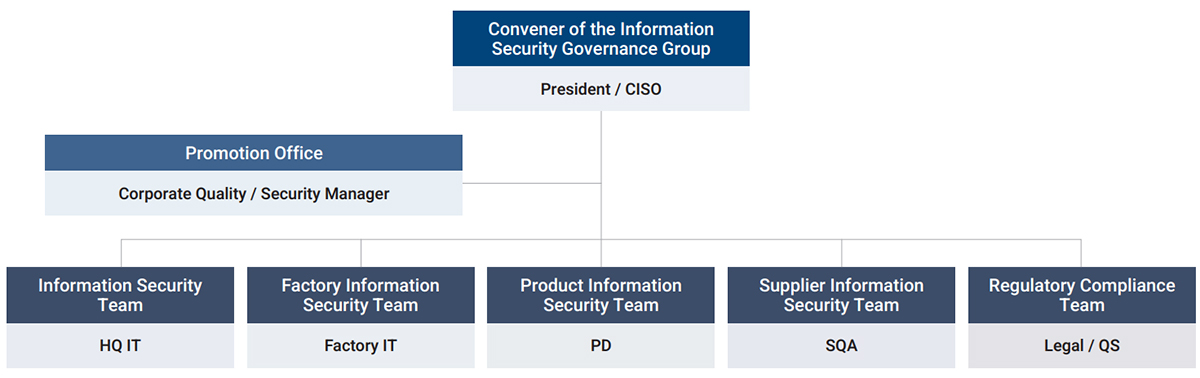
Information security is the cornerstone of Advantech’s corporate governance. We are committed to safeguarding our operations, products, services, and customer data with the highest standards. To strengthen the effectiveness of supervision and governance, the Board of Directors monitors the overall information security risks and major developments through the Risk Management Committee. The president also concurrently serves as the Chief Information Security Officer (CISO) to coordinate Advantech’s overall information security strategies, showing our highest-level commitment to information security.
With the support of senior executives, Advantech has established a cross-departmental Information Security Governance Team, which is jointly operated by the Information, Quality Assurance, and Information Security Teams, and is responsible for computer information, physical environment, product information security, supply chain security, and compliance. The Information Security Governance Team convenes quarterly meetings to review management results, major information security issues, and information security strategy directions, and regularly reports to the Risk Management Committee. This makes information security governance part of the enterprise risk management and operational decision-making process, implementing top-down governance responsibilities and supervision mechanisms, which improves the overall resilience of operations and the maturity of sustainability governance.
Organization Structure of Information Security Team
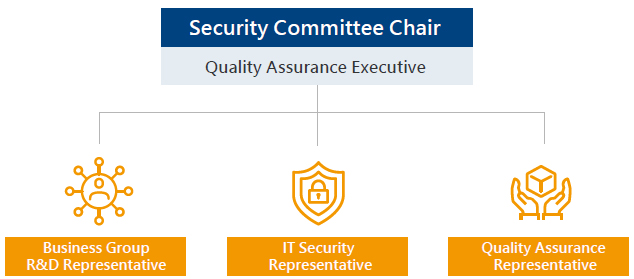
Furthermore, to enhance the management of product-related security issues, the Company established a Cybersecurity Committee in October 2024. The Committee is composed of representatives from the R&D departments of various business units, IT and cyber security, Quality Assurance, and other relevant functions, with the executive of the QA unit serving as Chairperson. The Committee convenes regularly to address matters related to the Company’s products, including regulatory compliance, vulnerability management, development processes, and overall governance.
Completed the transition to ISO/IEC 27001:2022 in China, North America, and Europe in 2025
At the same time, Advantech is working to make the systems of regional locations more consistent worldwide, so that all business units around the world can meet information security control requirements of the new version standard.
Since obtaining the ISO/IEC 27001 Information Security Management System (ISMS) certification in 2019, we have continued to improve various information security management measures to meet the requirements of international standards, and maintain the validity of the certificate and maturity of the management system through internal and external audits. Server room management by IT at the headquarters, the backbone network, and OT operations of the Linkou Plant successfully completed the transition to ISO/IEC 27001:2022 in 2024. We have comprehensively implemented improvement measures in terms of strategy, management, technology, and personnel awareness according to the control requirements of the new version standard, increasing the depth of information security governance and the breadth of management at the organizational level.
Information and Cyber Security Management Strategy
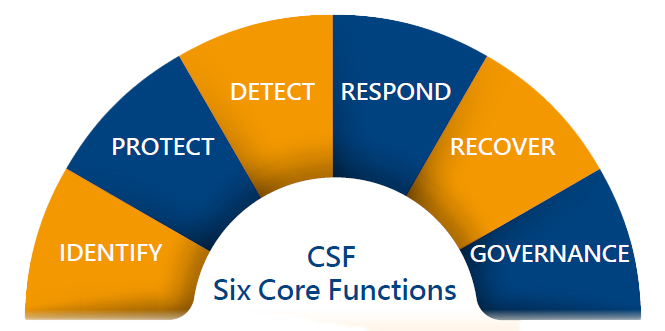
As the adoption of emerging technologies accelerates, Advantech has also closely monitored the risks and challenges brought by cloud-based, AI application, edge computing, and industrial control information security. Based on NSIT’s CSF of “Identification, Protection, Detection, Response, and Recovery,” we have developed comprehensive management strategies for corporate information security, operational technology security (OT Security), and cloud information security.
In accordance with the United States Securities and Exchange Commission’s (SEC) rules on cybersecurity risk management, governance, and incident disclosure by listed companies, we regularly conduct cybersecurity risk assessments, oversee the cybersecurity risks of third party service providers, and have response procedures and cyberattack recovery plans in place in the event of a cybersecurity incident.
In addition, Advantech actively participates in information security intelligence sharing organizations, such as the Taiwan Chief Information Security Officer Alliance and TWCERT/ CC, to obtain early warnings, threat intelligence, and vulnerability intelligence in real-time. This enables it to quickly understand external risks and take response measures in advance. At the same time, Advantech continues to improve the maturity of overall information security governance, strengthen the resilience of business operations, and build a trustworthy global brand through continuous information security risk assessment, third-party supplier risk monitoring, compliance with laws and regulations, and product information security management mechanisms implemented by the Cybersecurity Committee.
Raising Employees' Information Security Awareness
A total of 7,734 participants received 3,867 hours of employee information security training in 2025
Advantech has included information security as a required course each year to raise employees' information security awareness. The e-learning course mainly covers and includes tests on common information security risks and response methods, Advantech's information security policies and regulations, prevention of ransomware and phishing e-mails, software security control, and information security incident reporting.
In the phishing e-mail drill, the headquarters and overseas subsidiaries all performed better in 2025 compared to last year, indicating that employees are more alert to phishing e-mail attacks
- A total of 15,927 phishing e-mails were sent
- The pass rate of employees at the headquarters was 88.9% (81.7% in 2024)
- The pass rate of employees of overseas subsidiaries was 90.9% (77.4% in 2024)
Advantech sent phishing e-mails similar to those sent by hackers to employees at the headquarters and overseas subsidiaries twice (initial test and second test), and provided online courses and tests to make employees more alert to phishing e-mail attacks and improve their ability to respond.
In addition to the aforementioned information security training courses and social engineering drills, information security e-newsletters were sent to employees worldwide every quarter in 2025. The contents included important announcements, case studies, and key work results.
Advantech also revised the “Information Security Reward and Punishment Management Regulations” in 2025, imposing fair and effective penalties for violations of information security policies and procedures. The regulations provide incentives to personnel who effectively avoid information security incidents, and also serve as a way of alerting employees who may neglect information security procedures in other situations, raising the information security awareness of all employees, and effectively preventing the occurrence of information security incidents.
System Disaster Recovery Drills
The 2025 drill for the disaster recovery (DR) system aimed to verify whether Advantech could restore core IT services within an acceptable timeframe when a major disaster or system interruption occurred, and to ensure the feasibility of various backup mechanisms and recovery processes. Before the drill, the scope of the drill was clearly defined in accordance with the DR SOP, including databases, key application systems, identity verification, DNS, RADIUS, file services, virtualization platforms, and hybrid/relay services. The drill was initiated according to the plan, including network routing adjustment, backup station VM startup, DR DB/DR AP activation, and necessary load balance or firewall policy synchronization measures. After the switch was completed, service owners immediately performed verification. After the drill was completed, each team summarized the test results, deficiencies, and improvement recommendations, and included them in the DR Report so that supervisors could review and use the results as the basis for improving the drill and backup strategies for the following year. Overall, the 2025 DR Drill successfully verified Advantech’s maturity in terms of remote backup mechanism, network switching, data synchronization, disaster scenario simulation, and service effectiveness. At the same time, areas with room for improvements were identified through the review of deficiencies, such as the degree of automation, consistency of the backup environment, and standardization of complex system processes. The annual DR Drill not only ensures that the IT infrastructure can maintain business continuity when unexpected events occur, but also allows teams to accumulate experience, shortens the recovery time, lowers the risk of business interruption, and continues to enhance overall information resilience.
Supply Chain Information Security Management
Advantech randomly selects and audits major suppliers with potential information security risks each quarter. Cross-validation of suppliers’ information security maturity is performed via a questionnaire survey and external information security rating services. Evaluation results are provided to procurement and quality departments as the basis for subsequent management. If a supplier is involved in remote maintenance, system development, or has access to Advantech’s network, it must comply with our security requirements (such as encrypted transmission, access control, anti-virus updates, and VPN control) and participate in information security awareness campaigns or accept equipment inspections as needed. The management processes described above enable us to monitor the information security risks of suppliers. Advantech requires suppliers to make improvements and may cease cooperation with a supplier when an abnormality is discovered. This is to ensure the information security resilience of the overall supply chain and reduce the impact of third party vulnerabilities on business operations. A total of 80 suppliers completed the information security risk self-assessment this year. Twelve suppliers were randomly selected and their implementation of information security management was inspected.
Information Security Incidents in Recent Years
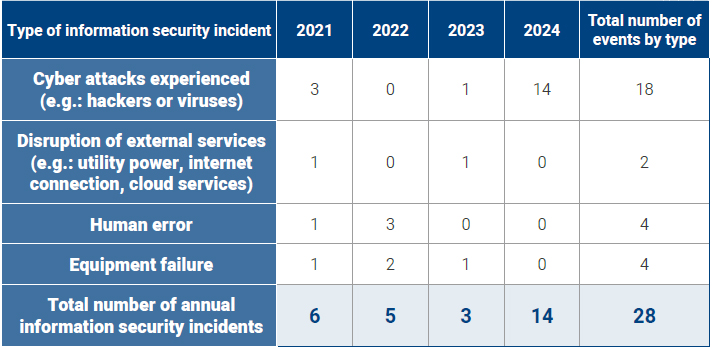
A total of 3 cyberattacks occurred in 2025, but none of them had a significant impact on operations. One of the incidents was a social engineering incident, and the other 2 were suspected hacking or malware. Among the information security incidents mentioned above, we only engaged an external professional unit to investigate and handle one of the incidents, resulting in a financial impact of less than NT$300,000.From 2021 to 2025, the company experienced zero major cybersecurity incidents, with no data breaches recorded. After completing root cause analysis, the IT department continued to optimize endpoint protection capabilities and calibrated the performance of anti-virus and detection tools. It also provided enhanced training for employees to identify phishing e-mails and suspicious links. At the same time, we continue to regularly organize social engineering drills and training sessions to raise all employees' awareness and ability to counter fraud. We have continually built a more resilient information security environment through the enhanced measures mentioned above, and protected operations and information assets through preventive management mechanisms. In addition, regarding reporting and handling methods for information security incidents, external stakeholders (such as customers and suppliers) may notify our IT department through the contact person if their personal data or rights and interests are damaged due to an information security incident. If an internal employee suspects that an information security incident has occurred, the employee can report it through IT.Security@advantech.com.tw.